Our Layered Approach to Protecting Your IT Environment
- Identity-first controls, including MFA, single sign-on and role-based access, help prevent unauthorised users from reaching critical systems.
- Next-generation firewalls, endpoint protection, encryption and regular patching protect your IT assets across on-premises, branch and hybrid environments.
- Our 24x7 SOC monitors networks, devices and cloud workloads for unusual activity, supported by SIEM, SOAR and threat intelligence.
- Structured incident response, backup and recovery processes help restore systems quickly and minimise disruption when an incident occurs.
Network Security
- We design layered network defences aligned to Zero Trust principles, protecting on-premises, branch and hybrid environments from unauthorised access.
- Next-generation firewalls, IDS/IPS, advanced threat prevention and encrypted traffic inspection (TLS 1.3) help identify and block malicious traffic.
- Secure SD-WAN, SASE and ZTNA extend consistent security to remote users and branch offices, supported by network access control and micro-segmentation.
- Network Detection and Response (NDR) and AI-powered threat prevention provide real-time visibility into unusual traffic patterns and potential incidents.
Endpoint Security
- We protect laptops, desktops, servers and mobile devices with real-time protection powered by behavioural AI and global threat intelligence.
- EDR and unified XDR platforms help detect, contain and remediate attacks, with automated rollback to support recovery from ransomware.
- Next-generation antivirus, device encryption and data loss prevention help safeguard sensitive information on managed devices.
- Mobile Device Management (MDM/UEM) and patch and vulnerability management provide centralised visibility and control across your device estate.
Cloud Security
- We help secure your AWS, Azure and GCP environments through secure architecture, posture management and workload protection under the shared-responsibility model.
- CSPM, CWPP and unified CNAPP platforms provide continuous visibility, with AI-assisted detection of misconfigurations before they lead to breaches.
- Cloud Infrastructure Entitlement Management (CIEM) controls who can access your cloud resources and which actions they can perform.
- Container and Kubernetes security, DevSecOps and Infrastructure-as-Code scanning help your teams innovate securely, with continuous compliance reporting.
Identity & Access
Management (IAM)
- Our identity platforms help ensure only authorised users, devices and applications can access your critical systems, applying Zero Trust principles throughout.
- Single sign-on, multi-factor authentication and passwordless options such as passkeys and FIDO2 strengthen security while simplifying the user experience.
- Privileged Access Management (PAM) and Identity Governance and Administration (IGA) apply least-privilege access and maintain audit-ready controls.
- Adaptive, risk-based access and Identity Threat Detection and Response (ITDR) help reduce credential-based attacks, including those targeting machine and AI-agent identities.
Security Operations
Center (SOC)
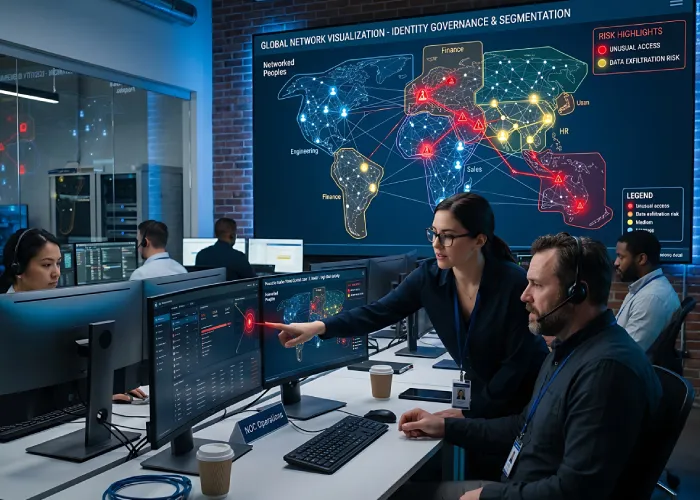
- Our 24x7 Security Operations Center monitors your environment around the clock, combining SIEM, SOAR and threat intelligence with experienced security analysts.
- We handle SIEM deployment and use-case engineering, with SOAR playbooks that automate routine response actions and reduce analyst workload.
- AI-assisted analytics, UEBA and XDR integration support proactive threat hunting and help reduce the time taken to detect and respond to incidents.
- Incident response, forensics support and compliance dashboards give you enterprise-grade security operations without the cost of building an in-house SOC.
Vulnerability Assessment & Penetration Testing (VAPT)
- Our certified ethical hackers identify vulnerabilities across your networks, web and mobile applications, APIs, cloud and wireless environments, and help you remediate them.
- We combine automated scanning with expert manual testing to uncover exploitable flaws, misconfigurations and outdated components.
- Findings are prioritised by risk, with clear remediation guidance, retesting and CERT-In aligned reporting to support audit requirements.
- Continuous Threat Exposure Management (CTEM), Attack Surface Management and AI-assisted prioritisation provide an ongoing view of your exposure.
Our Methodology
A Structured Approach to Stronger Information Security
Govern
Establish security policies, roles and risk strategy aligned with your business objectives.
Identify
Map assets, risks and vulnerabilities across your IT environment.
Protect
Apply firewalls, encryption, access controls and secure configurations to safeguard critical systems.
Detect
Monitor networks, endpoints and cloud workloads continuously to identify threats and anomalies.
Respond
Contain incidents quickly, investigate the root cause and execute your response plan.
Recover
Restore systems, apply lessons learned and strengthen controls to improve resilience.
Benefits of Information
Security for Businesses
- Protect Confidential Data
- Reduce Exposure to Cyber Attacks
- Support Business Continuity
- Build Customer Trust
- Support Regulatory Compliance
- Reduce Financial Risk
- Strengthen Access Control
- Improve Risk Management
- Protect Business Reputation
Trusted Where Security
Matters Most
Security solutions tailored to the risks and regulatory needs of each sector
Corporates
Manufacturing
IT/ITeS
Government
Education
Media
Hospitality
Healthcare
FAQ's
What is IT security?
IT security protects your organisation’s data, systems, networks and devices from cyber attacks, breaches and unauthorised access.
Why does my business need IT security?
It protects sensitive information, reduces cyber risk, supports regulatory compliance and helps maintain the trust of your customers and partners.
Which IT security services does FortRise offer?
We offer network, endpoint, cloud and identity security, a 24x7 Security Operations Center, and vulnerability assessment and penetration testing.
How does FortRise protect business data?
We combine encryption, identity and access controls, endpoint protection, continuous monitoring and regular vulnerability assessments within a layered, Zero Trust approach.
How does FortRise support compliance?
We align security controls with frameworks such as ISO 27001, NIST CSF 2.0 and CERT-In guidelines, and provide reporting to support your audits.
Trusted Technology Partners
Certified partners of leading global security and technology providers